

Client Credentials Grant Type in OAuth 2.0
The Client Credentials Grant Type is specifically designed for applications that need to access resources not associated with a particular user. In this scenario, the client acts as the resource owner. This grant type is most appropriate for back-end systems where the application interacts with a service without any user context.
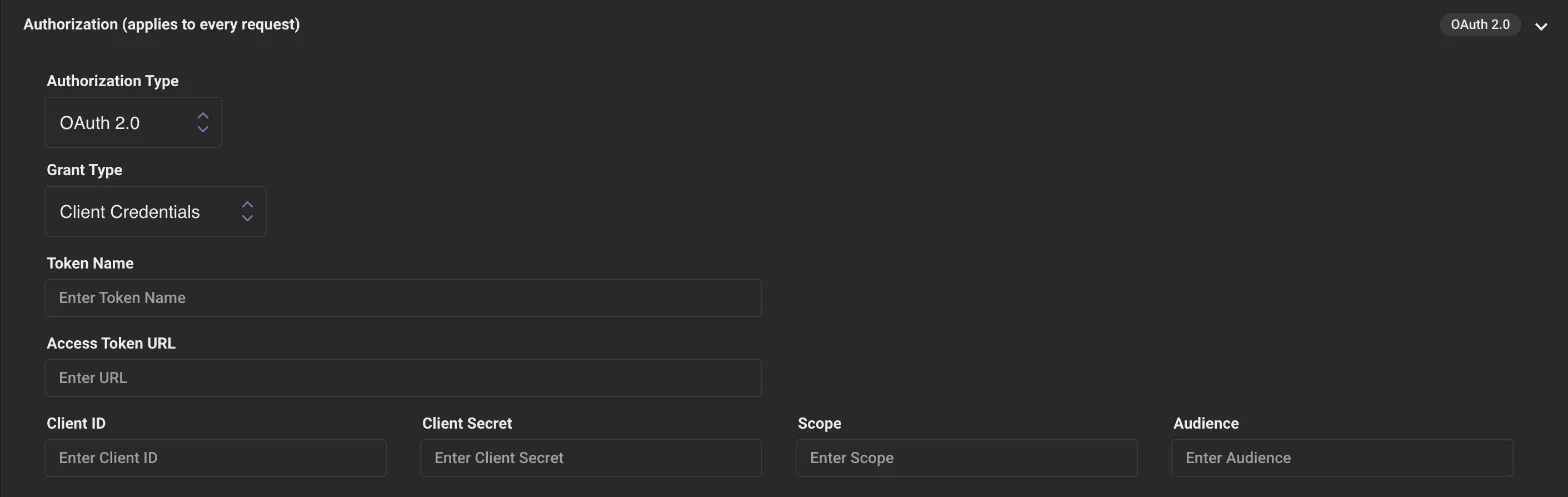
What You Enter in LoadFocus
Section titled “What You Enter in LoadFocus”In a load test, set Authorization Type to OAuth 2.0 and Grant Type to Client Credentials. The form has these fields:
- Token Name: a label for you. It is not sent to the server.
- Access Token URL: the provider's token endpoint.
- Client ID, Client Secret: the credentials of your registered client.
- Scope: the permissions to request, if your provider uses them.
- Audience: only needed by providers that ask for it (it is not part of RFC 6749).
Before the test starts, LoadFocus sends one POST request to the Access Token URL over HTTPS, with the fields above as a JSON body, and reads access_token from the JSON response. RFC 6749 describes a form-encoded body, so if your provider rejects the request, check whether its token endpoint accepts JSON.
How It Works
Section titled “How It Works”Requesting the Token:
Section titled “Requesting the Token:”- The client sends a request to the authorization server. This request usually includes the client's
client_idandclient_secretto authenticate itself.
Token Response:
Section titled “Token Response:”- After successfully authenticating the client, the authorization server issues an access token. The client can then use this token to request resources from the resource server.
Configuring the Client Credentials Grant
Section titled “Configuring the Client Credentials Grant”Register Your Application:
Section titled “Register Your Application:”- Begin by registering your application with the OAuth 2.0 provider. After registration, you should receive a
client_idandclient_secret.
Token Request:
Section titled “Token Request:”- Your application needs to send a POST request to the token endpoint of the authorization server. This request should include the
grant_typeparameter set to "client_credentials", and theclient_idandclient_secret. It's crucial to send this request securely, using HTTPS.
Handle the Token Response:
Section titled “Handle the Token Response:”- The authorization server will respond with an access token once it verifies your application. Handle this token securely within your application.
Use the Token:
Section titled “Use the Token:”- With the access token in hand, your application can send authorized requests to the resource server to access the allowed resources.
Points to Consider
Section titled “Points to Consider”-
No User Interaction: This grant type does not involve end-user authentication, making it suitable for server-to-server interactions.
-
Security: Given that application credentials (
client_idandclient_secret) are essential for obtaining the token, it's imperative to keep them secure. Any security lapse could lead to unauthorized access. -
Limited Scope: Tokens acquired via this flow should be limited in their scope, granting only the permissions necessary for the application to function.
Conclusion
Section titled “Conclusion”The Client Credentials Grant Type provides an efficient way for applications to communicate with a service without user intervention. It's the usual choice for situations where an application needs to operate on its own behalf, not on behalf of a user. However, developers need to be cautious and ensure the security of the application's credentials to prevent potential security risks.