Response Time Limits
API Check Limits - Response Time Limits
What are Response Time Limits?
Response time limits allow you to define thresholds for marking an API check as degraded or failed based on how long it takes to receive a response. This helps in identifying performance issues early and taking necessary actions to maintain optimal API performance.
How to Configure Response Time Limits
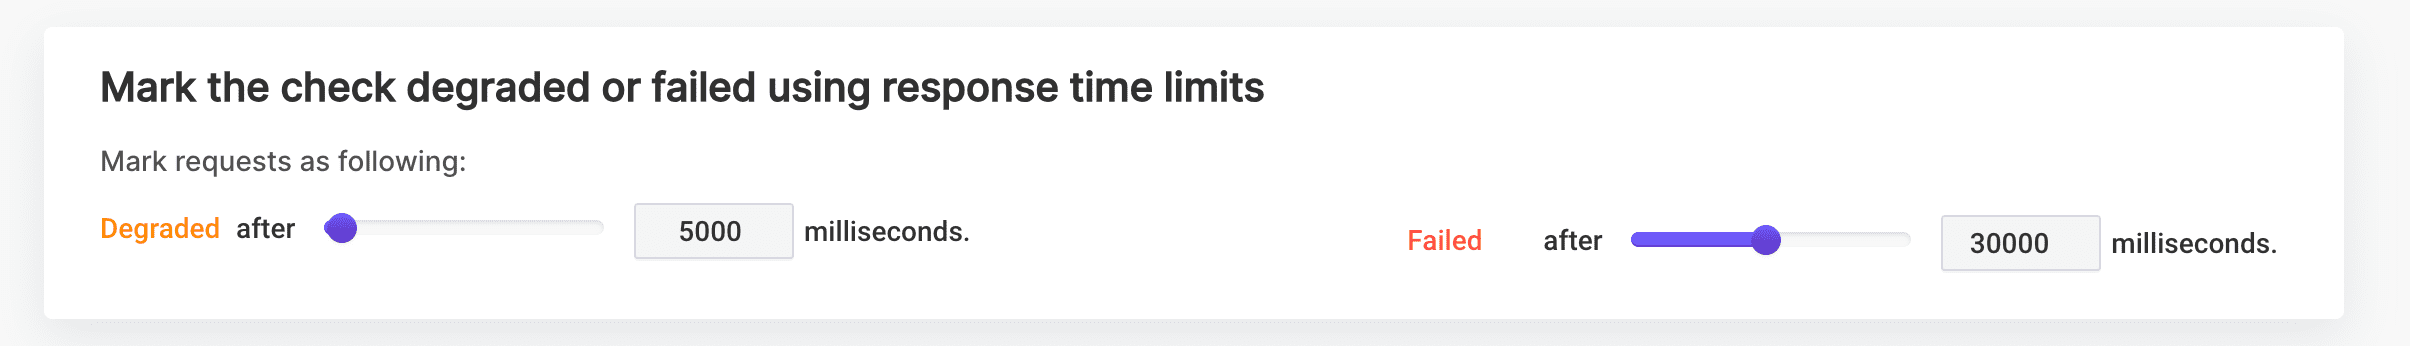
In the check form, find Mark the check degraded or failed using response time limits. The limits are compared with the total response time of the HTTP request (all phases added up). TCP and DNS checks have their own Degraded threshold (ms) setting instead.
- Degraded after: Mark the check as degraded if the response time exceeds this many milliseconds (default 5000). This indicates that the API is still functioning but not performing optimally.
- Failed after: Mark the check as failed if the response time exceeds this many milliseconds (default 30000, maximum 60000). This indicates that the API is not performing as expected and needs immediate attention.
If the API check is both degraded and failed based on the response time limits, it will be marked as failed. This ensures that any severe performance issues are promptly highlighted.
Practical Use Cases
- Performance Monitoring: Set thresholds to monitor and maintain API performance. For example, mark an API as degraded if the response time exceeds 2000ms and failed if it exceeds 5000ms.
- Early Warning System: Use degraded limits as an early warning system to identify potential performance issues before they escalate into failures.
- Service Level Agreements (SLAs): Ensure that your API meets the response time requirements specified in your SLAs by setting appropriate limits.
Degraded and failed checks trigger alerts like any other result; choose where they go in alert channels.